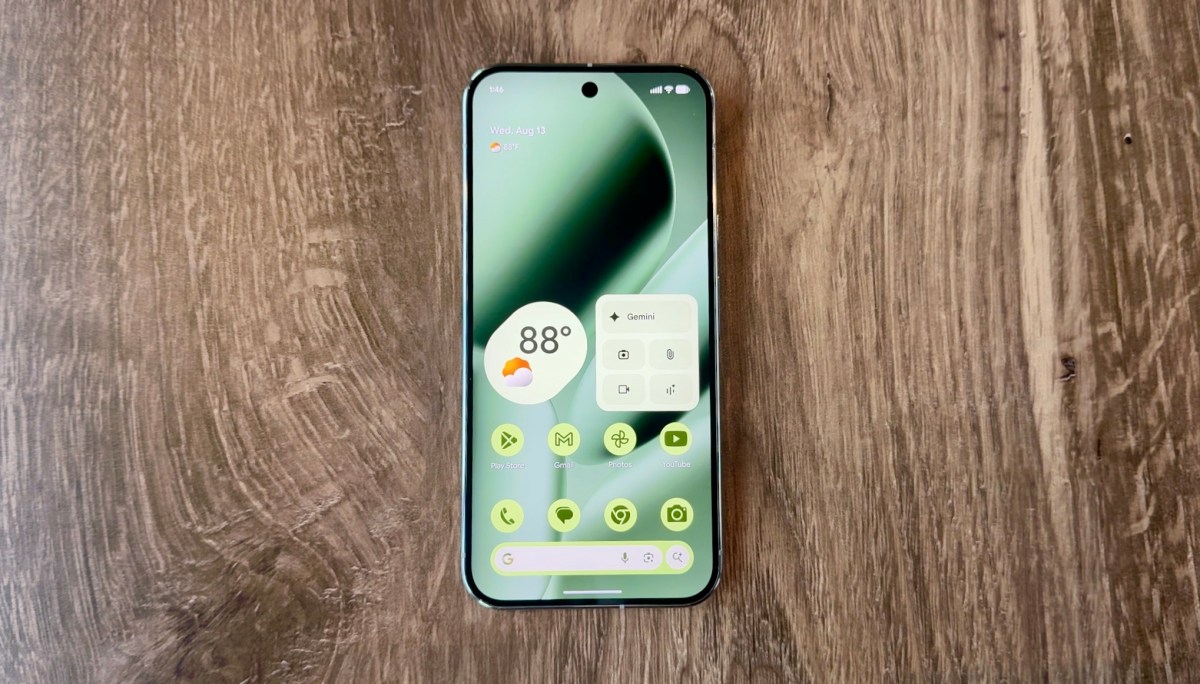
Google has issued a warning that a subset of its Pixel phone owners may have fallen victim to a zero‑day attack. The company stated that evidence points to a flaw in the device’s modem that “may be under limited, targeted exploitation.” While the exact nature of the vulnerability remains under investigation, the announcement signals a serious security concern for the Pixel line.
The modem is the component that handles cellular communications, and a weakness there can allow attackers to intercept data or gain unauthorized access to the device. Zero‑day vulnerabilities are particularly dangerous because they are unknown to the vendor and can be exploited before a patch is released. In this case, Google’s own security team has identified indications that the flaw has already been leveraged, albeit in a restricted manner.
What does this mean for Pixel owners? First, it underscores the importance of keeping devices updated. Google typically releases security patches through its monthly update cycle, and users who have delayed applying those updates may be more exposed. Second, it highlights the need for vigilance against suspicious network activity, as attackers could be attempting to exploit the modem to gain a foothold.
The company has not provided a detailed technical description of the bug, nor has it disclosed the exact number of affected devices. Nevertheless, the use of the term “limited, targeted exploitation” suggests that the attack may have been directed at specific users or regions rather than a broad, mass‑scale intrusion.
In the broader context of mobile security, this incident is a reminder that hardware components, not just software, can harbor critical vulnerabilities. Modems, which often run on proprietary firmware, are a common target for attackers seeking to bypass higher‑level security controls.
Google’s response has involved working with its security researchers to assess the scope of the problem and to develop a fix. While the company has not yet released a patch, it has urged users to monitor official channels for updates and to install any forthcoming security releases promptly.
The potential impact extends beyond individual users. If the flaw allows for data interception or device compromise, it could affect sensitive communications, personal data, and even financial transactions. For businesses that rely on Pixel devices for corporate communications, the risk is amplified.
In summary, Google’s announcement of a possible zero‑day attack on the Pixel modem serves as a cautionary tale. It emphasizes the ongoing battle between device manufacturers and cyber adversaries and the critical need for timely updates and proactive security practices among users.